VULNIX0 / CASE FILEMODULE 13 — THREAT INTEL
MODULE 13 OF 16
Threat Intel
Threat-intel feeds are only as useful as the asset inventory they're checked against. Vulnix0 builds that inventory first through continuous discovery, then runs the correlation automatically every time the feeds update, not just on the day someone remembers to run the report.
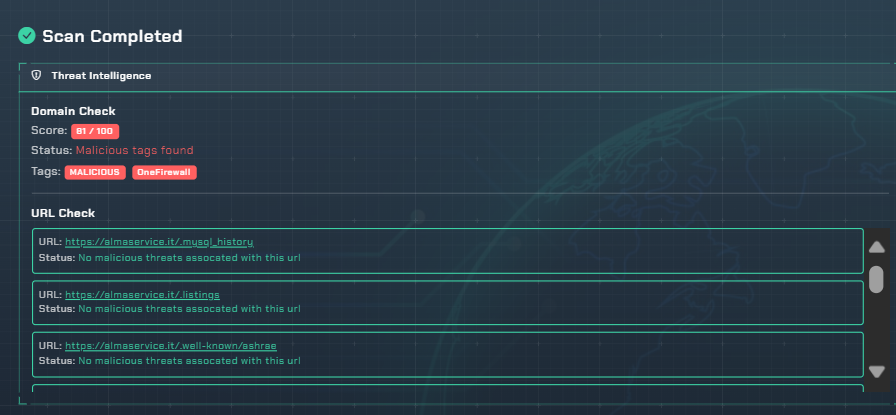
Exhibit — Threat Intel output, Vulnix0 dashboard
What We Check
Module 13 — checklist
✓Asset inventory as the foundation for every intel correlation
✓Real-time feed ingestion across multiple reputation sources
✓Risk scoring per asset based on threat-feed association
✓Alerting when a previously clean asset gets flagged
✓Historical trend view of your domain and IP reputation
✓Exportable evidence for incident-response workflows
VULNIX0 / CASE FILECLOSE
Close the File
Find out what an attacker would find. Today.
Request access, or talk to the team behind Vulnix0.
The first project out of Velocity Lab — OneFirewall Alliance's R&D team — built with AquilaX Security. AI-driven offensive security, from discovery to continuous exploit validation.