VULNIX0 / CASE FILEMODULE 11 — OPEN PORT ANALYSIS
MODULE 11 OF 16
Open Port Analysis
Every open port is a door, and most organizations don't have an accurate count of how many they're leaving unlocked. Vulnix0 enumerates the full TCP range across every resolved IP, fingerprints what's actually listening on each one, and flags databases, remote-management interfaces, and IoT/ICS protocols that have no reason to be internet-facing.
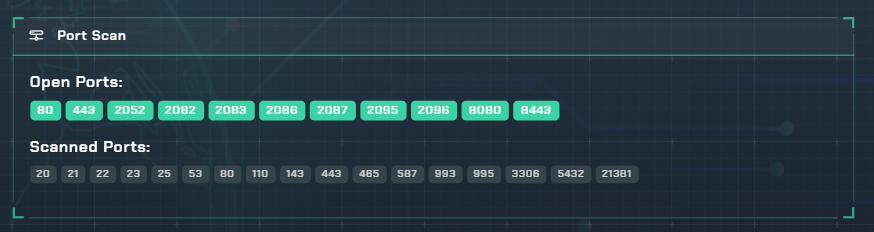
Exhibit — Open Port Analysis output, Vulnix0 dashboard
What We Check
Module 11 — checklist
✓Full TCP port enumeration across all resolved IPs
✓Service and banner fingerprinting on every open port
✓Insecure-protocol flagging — FTP, Telnet, unencrypted mail
✓Exposed database and cache detection — Redis, MongoDB, Elasticsearch
✓Remote-management interface exposure — VNC, WinRM, RDP
✓IoT/ICS protocol exposure — MQTT, Modbus, RTSP, DICOM
VULNIX0 / CASE FILECLOSE
Close the File
Find out what an attacker would find. Today.
Request access, or talk to the team behind Vulnix0.
The first project out of Velocity Lab — OneFirewall Alliance's R&D team — built with AquilaX Security. AI-driven offensive security, from discovery to continuous exploit validation.