VULNIX0 / CASE FILEMODULE 10 — OFFENSIVE SECURITY ASSESSMENTS
MODULE 10 OF 16
Offensive Security Assessments
A spreadsheet of CVEs ranked by CVSS is not an assessment of your actual risk. Vulnix0 correlates findings across every module — a leaked credential here, an exposed admin panel there — into the kind of attack path a human red teamer would reconstruct, then validates whether that path actually closes.
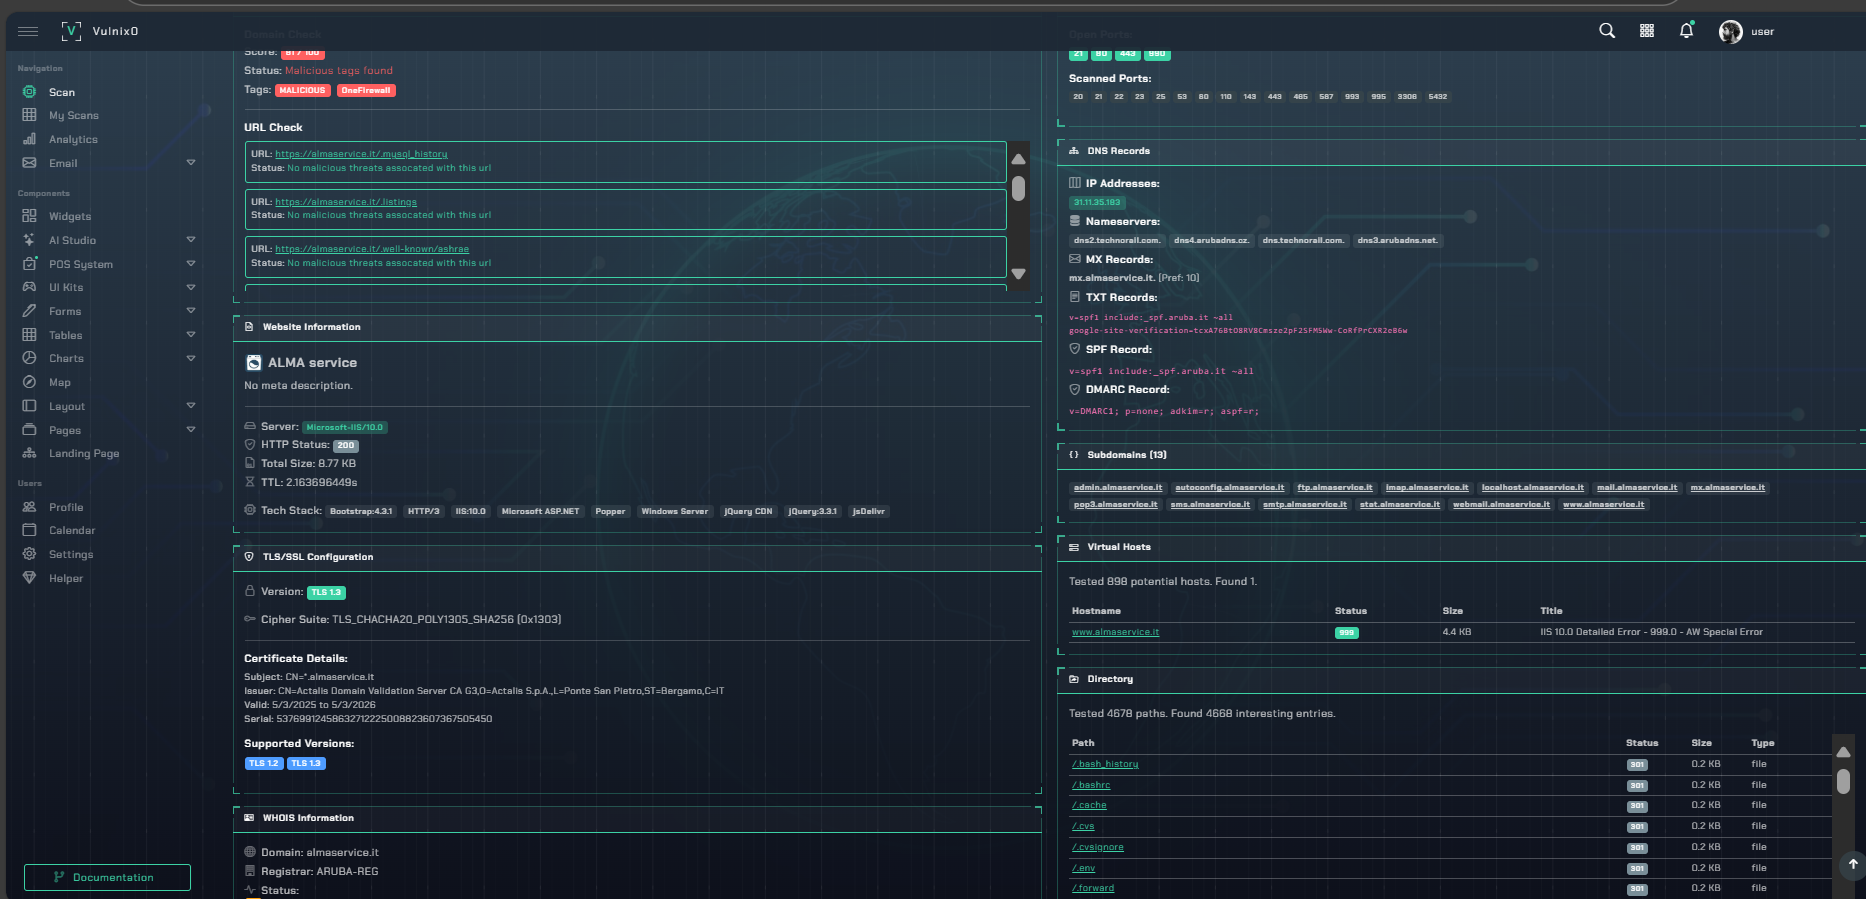
Exhibit — Offensive Security Assessments output, Vulnix0 dashboard
What We Check
Module 10 — checklist
✓Finding correlation across recon, web, and infrastructure modules
✓Attack-path construction from chained, individually low-severity issues
✓Red-team methodology applied at automated scale
✓Exploit validation with reproducible evidence, not theoretical CVSS
✓Business-impact-aware prioritization of what to fix first
✓Continuous re-assessment as your environment changes
VULNIX0 / CASE FILECLOSE
Close the File
Find out what an attacker would find. Today.
Request access, or talk to the team behind Vulnix0.
The first project out of Velocity Lab — OneFirewall Alliance's R&D team — built with AquilaX Security. AI-driven offensive security, from discovery to continuous exploit validation.