VULNIX0 / CASE FILEMODULE 08 — FILES DISCOVERY
MODULE 08 OF 16
Files Discovery
A forgotten .git directory or a config.old left on a production host is still one of the fastest ways to leak source code and credentials outright. Vulnix0 enumerates the paths attackers check within the first minutes of an engagement, and re-checks automatically as the crawler surfaces new ones.
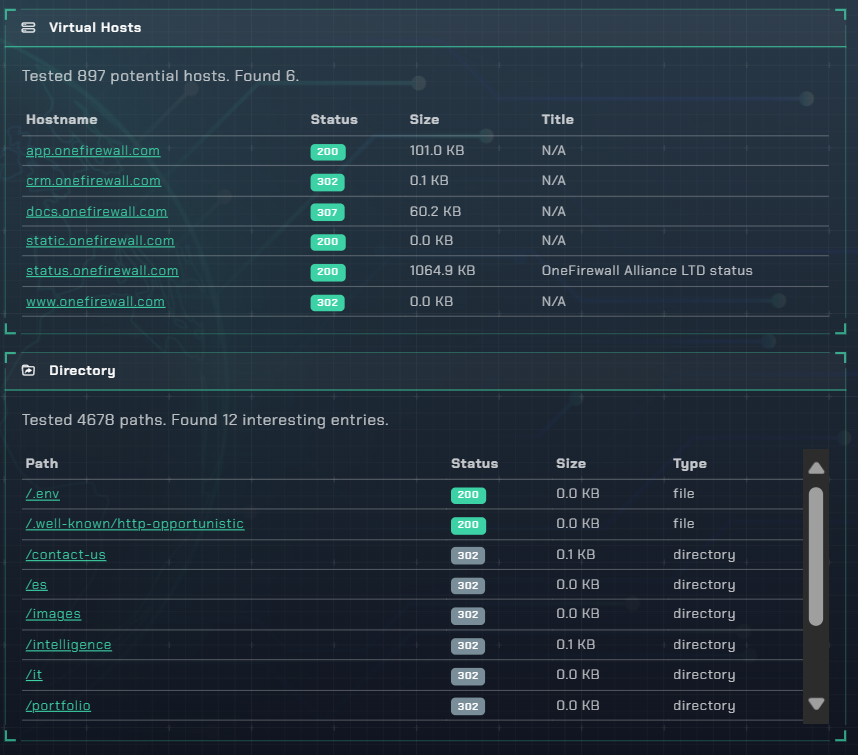
Exhibit — Files Discovery output, Vulnix0 dashboard
What We Check
Module 08 — checklist
✓Directory and file brute-force against a curated sensitive-path wordlist
✓Source control exposure — .git/config, .git/HEAD, .svn
✓Configuration and backup file detection (.env, config.old, .bak, .sql)
✓Status-code and content-type classification of every hit
✓Path-traversal probing on file-serving parameters
✓Automatic re-check as new paths are discovered by the crawler
VULNIX0 / CASE FILECLOSE
Close the File
Find out what an attacker would find. Today.
Request access, or talk to the team behind Vulnix0.
The first project out of Velocity Lab — OneFirewall Alliance's R&D team — built with AquilaX Security. AI-driven offensive security, from discovery to continuous exploit validation.