VULNIX0 / CASE FILEMODULE 04 — DYNAMIC APPLICATION SECURITY TESTING (DAST)
MODULE 04 OF 16
Dynamic Application Security Testing (DAST)
Vulnix0's crawler follows every link, form, and API call a real session would generate, builds a complete parameter map of the application, and fuzzes each one for injection, authorization, and logic flaws as they behave at runtime, not as a static analyzer guesses they might.
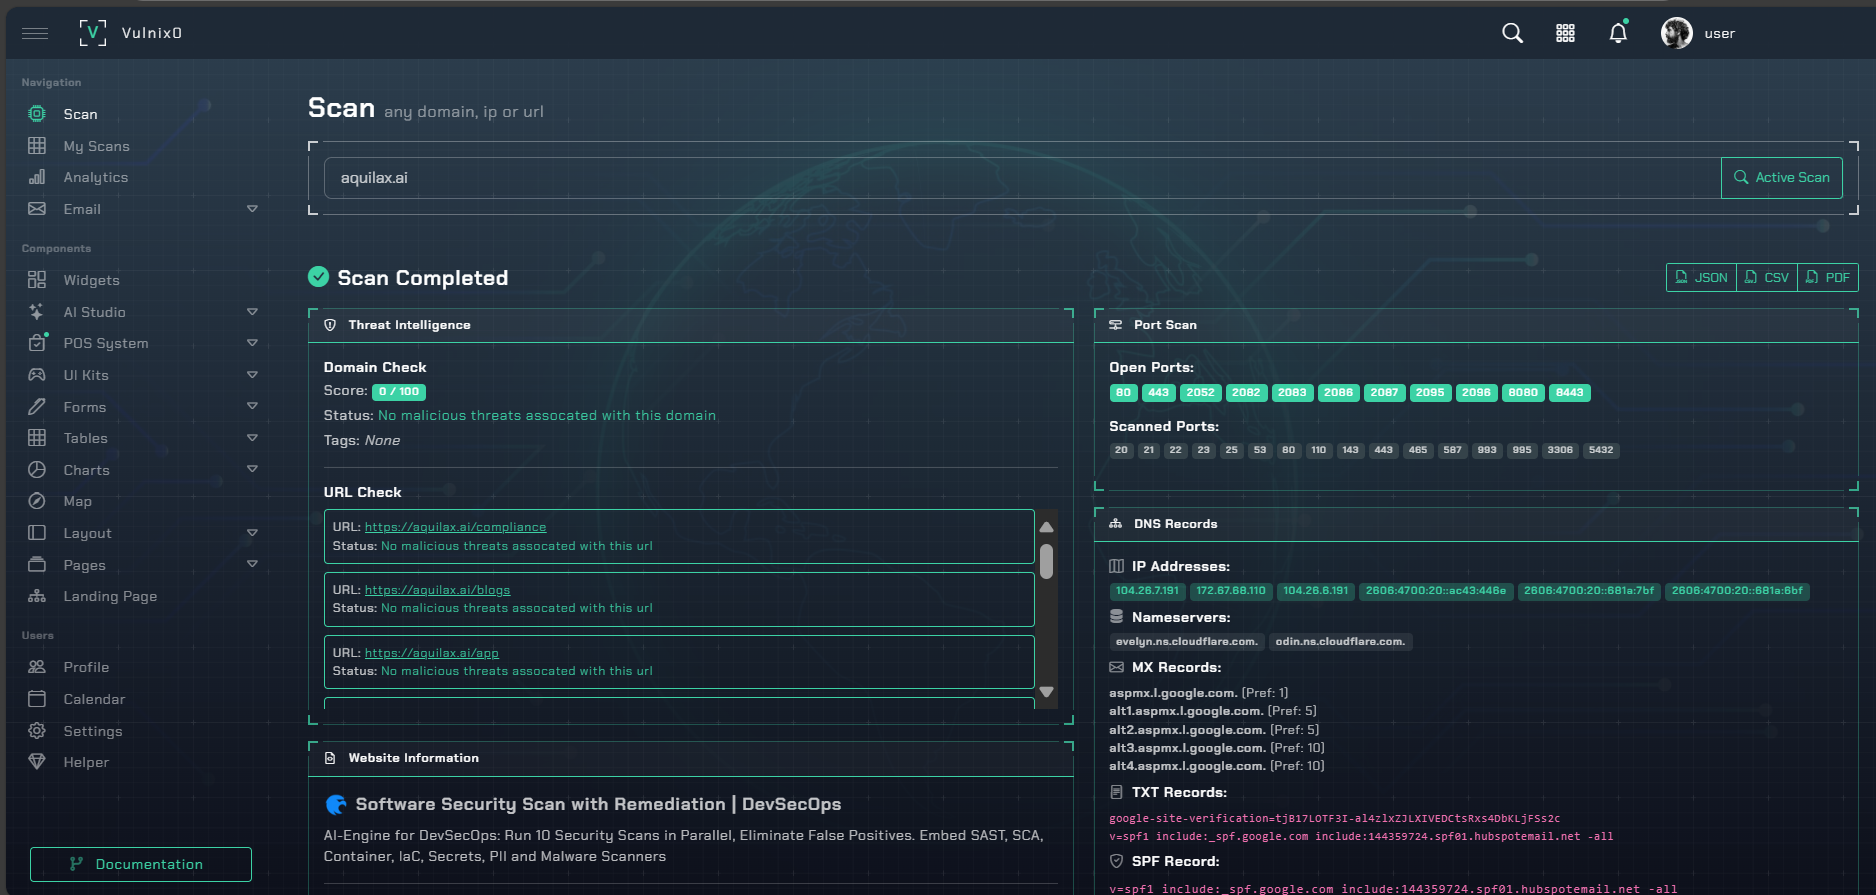
Exhibit — Dynamic Application Security Testing (DAST) output, Vulnix0 dashboard
What We Check
Module 04 — checklist
✓Crawl-driven injection testing — SQLi, XSS, SSTI, path traversal, command injection
✓Broken Object-Level Authorization (IDOR/BOLA) via sequential-ID probing
✓Security header and CSP configuration analysis
✓Cookie security attributes (Secure, HttpOnly, SameSite)
✓Open redirect, CORS misconfiguration, and CSRF exposure checks
✓Stored XSS validated by round-tripping payloads through the app
VULNIX0 / CASE FILECLOSE
Close the File
Find out what an attacker would find. Today.
Request access, or talk to the team behind Vulnix0.
The first project out of Velocity Lab — OneFirewall Alliance's R&D team — built with AquilaX Security. AI-driven offensive security, from discovery to continuous exploit validation.