VULNIX0 / CASE FILEMODULE 03 — AUTOMATED PENETRATION TESTING
MODULE 03 OF 16
Automated Penetration Testing
An open port is not a finding; it's a question. Vulnix0 answers it by attempting the exploit directly — anonymous FTP login, an unauthenticated Redis instance, a Kubernetes Dashboard with no RBAC — under a policy you control, and hands you the request and response as proof instead of a severity label.
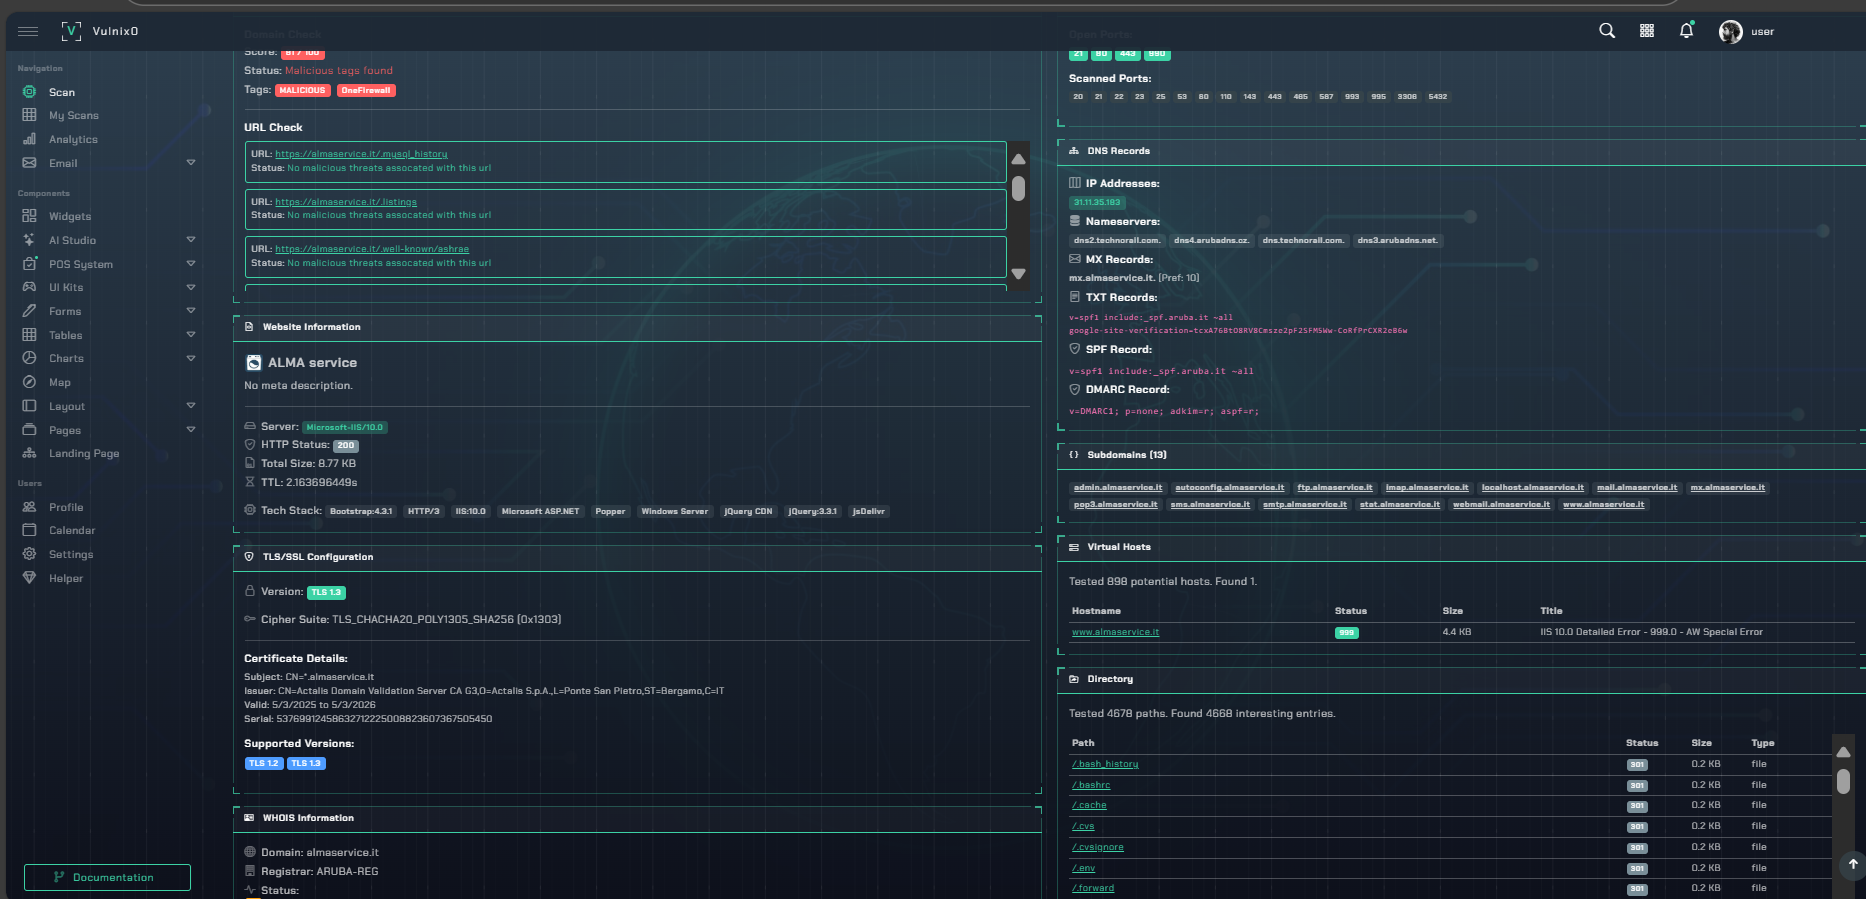
Exhibit — Automated Penetration Testing output, Vulnix0 dashboard
What We Check
Module 03 — checklist
✓SQL injection, XSS, path traversal, and command injection probing
✓Protocol-level checks: FTP anonymous login, SMTP open relay, unauthenticated Redis/VNC
✓Exposed AI/ML infrastructure: Ollama, MCP servers, vector databases
✓Kubernetes Dashboard, kubelet, and etcd unauthenticated-access checks
✓Policy-controlled aggressiveness — passive recon up to active exploit verification
✓Every finding ships with request/response proof, not a guess
VULNIX0 / CASE FILECLOSE
Close the File
Find out what an attacker would find. Today.
Request access, or talk to the team behind Vulnix0.
The first project out of Velocity Lab — OneFirewall Alliance's R&D team — built with AquilaX Security. AI-driven offensive security, from discovery to continuous exploit validation.